Practical cybersecurity learning | Hyderabad and online enquiries
SIEM Training in Hyderabad
Learn how security events become useful detections with SIEM Training in Hyderabad. Work through eight modules covering log ingestion, field mapping, searches, correlation, alert triage and tuning. Build a small detection portfolio using synthetic records and clear investigation notes.
Course outline8 modules
Practice3 project scenarios
DurationAsk for batch schedule
Course feeRequest current fee
About SIEM Training
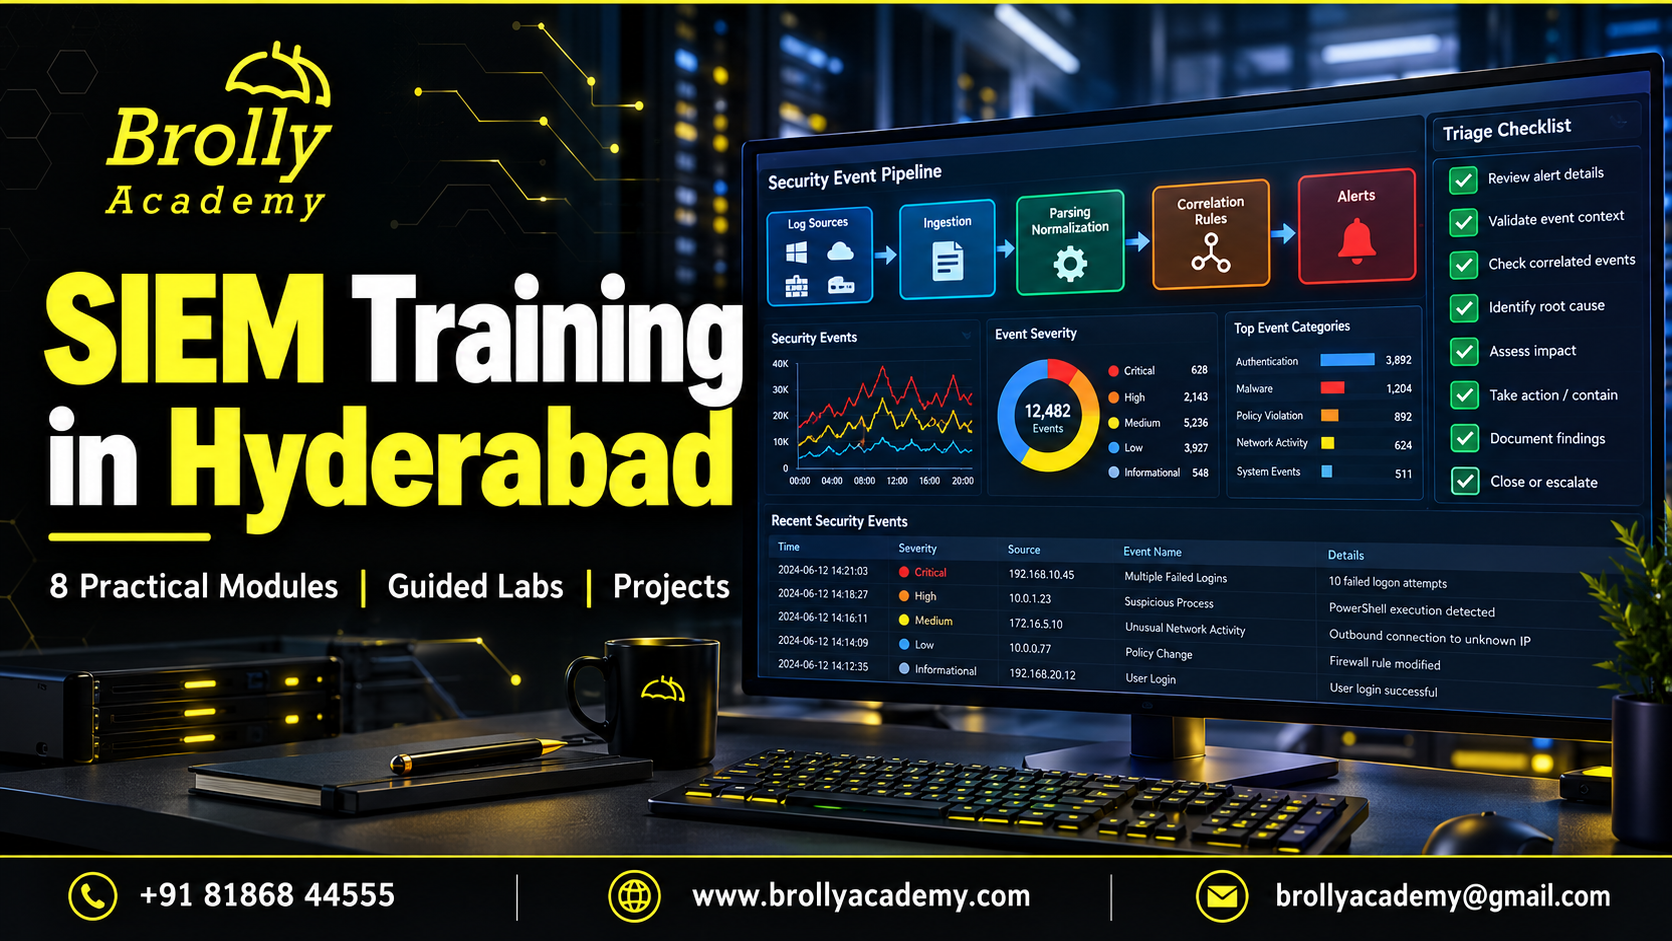
SIEM means Security Information and Event Management. A SIEM brings security-relevant records together so analysts can search, correlate and investigate activity. Useful results depend on reliable data, sensible detection logic and a person who can explain what an alert means.
This course focuses on the log-to-detection workflow. The existing SOC Analyst course covers broader operations, while the Splunk course is a separate product-focused path. Microsoft Sentinel and Splunk terminology may be discussed, but the confirmed batch platform determines the practical interface and query language.
Use Microsoft Sentinel overview alongside the relevant modules. The practice examples on this page are original teaching scenarios, not claims of vendor approval or live client work.
Who Should Join?
Basic networking, operating-system logs and security concepts are helpful. New analysts should be comfortable reading a timestamp, username, event result and source address before building correlation rules.
Learners building a specialismBasic networking, operating-system logs and security concepts are helpful. New analysts should be comfortable reading a timestamp, username, event result and source address before building correlation rules.
IT and security professionalsUse the module outputs to compare this course with the tasks in your current or target role.
Teams planning practical learningDiscuss a lab-led program using approved systems, synthetic records and clear learning goals.
For complementary learning, explore SOC Analyst Course. Connect technical findings with monitoring, escalation and analyst workflows.
SIEM Syllabus: 8 Practical Modules
Each module connects a concept to an exercise and an output you can explain. Work through the foundations before attempting the integrated project.
1. SIEM architecture and use cases
Map data sources, collection, storage, searches and alerts in a small lab design. Define a security question before choosing a dashboard. Explain how SIEM, endpoint detection and response automation have related but different roles.
2. Log sources and collection health
Identify the events needed from identity, endpoint and network sources. Check time synchronization, missing records and ingestion delay. Build a source-health checklist so a silent dashboard is not mistaken for a quiet environment.
3. Parsing and field normalization
Map different event formats into useful fields. Preserve the original record and record parsing failures. Compare source time with ingestion time and explain how an incorrect field mapping can break a detection.
4. Search and investigation queries
Practise filtering, grouping and ordering synthetic events in the agreed platform. Write an investigation question beside each query. Check assumptions about case, null values and time windows before drawing a conclusion.
5. Correlation and detection design
Turn one scenario into explicit logic with data dependencies and expected results. Include a benign case as well as a suspicious one. Explain why an alert is a hypothesis for investigation, not automatic proof of an incident.
6. Triage, enrichment and case notes
Review a lab alert with asset and account context. Record confidence, impact and a recommended escalation path. Keep the evidence concise enough for another analyst to follow without repeating the entire search.
7. Tuning and measurable quality
Review false positives, missed test cases and overly broad exclusions. Change one part of a rule and compare results on a defined dataset. Track the reason for each exception so tuning does not silently remove useful coverage.
8. Detection portfolio and handover
Deliver a data-source map, documented query, detection test cases and a triage runbook. Record platform assumptions and maintenance needs. Present one limitation and a plan to improve the rule safely.
Discuss Your Learning Goals
Tell the team about your experience and preferred schedule. Book a free demo to discuss the course, lab access and the practical work expected from you.
Practical Skills You Will Develop
Use the exercises to build an explanation as well as a result. You should be able to show what you did, how you checked it and where the limits are.
Parsing and field normalizationMap different event formats into useful fields.
Search and investigation queriesPractise filtering, grouping and ordering synthetic events in the agreed platform.
Correlation and detection designTurn one scenario into explicit logic with data dependencies and expected results.
Triage, enrichment and case notesReview a lab alert with asset and account context.
Tools and Lab Requirements
Practice only on systems you own or have explicit permission to use. The course outline uses isolated labs and synthetic data. Agree the software versions, access period, hardware requirements and any licence or cloud charges before enrolling. Never upload employer logs, credentials or personal evidence to a public tool.
SIEM training workspaceConfirm whether the batch uses Microsoft Sentinel, Splunk or another approved environment.
Synthetic event setsUse prepared authentication, endpoint and network records with known expected outcomes.
Detection test registerKeep logic, data dependencies, positive/negative cases and tuning decisions together.
Keep MITRE ATT&CK red teaming guidance available when checking an exercise. Use the instructions for your installed version and authorized access level.
Your Learning Roadmap
Build confidence in stages. Practice time and your starting knowledge matter as much as the number of scheduled sessions.
1. Set up and understandCheck the prerequisites and lab access. Complete the first two modules and explain the basic workflow in your own words.
2. Build and investigateWork through the middle modules. Keep notes of errors, what you tried and the evidence that supported a fix.
3. Test and presentComplete the final modules and an integrated scenario. Present your output, validation and a short handover guide.
3 Practical Project Scenarios
These are teaching scenarios using approved lab systems and synthetic data. They are not claims about live client work or previous student results.
Log onboarding quality checkMap fields and diagnose missing or delayed events in a synthetic collection pipeline.
Authentication detectionCreate and test a bounded suspicious-sign-in scenario with benign examples and analyst notes.
Tuning and handover packCompare a rule before and after a justified change, then write the operational runbook.
How the Skills Work in Practice
A rule looks for repeated failed sign-ins, but the parser maps some failures as successful events. More complex alert logic will not fix that data problem.
First validate the raw records and field mapping, then rerun a known test dataset. Report what was detected, what was missed and why the corrected rule is ready for review.
Why Learn with Brolly Academy?
Choose a course that connects the subject to work you can actually demonstrate. Use a demo to discuss the learning path and decide whether it fits your starting point.
A connected learning pathThe eight-module outline moves from foundations to an integrated task. Each module identifies an output rather than leaving practice as a vague promise.
A practical local conversationSpeak to the Hyderabad team about your goals, availability and lab needs. Ask questions before committing to a course or a particular schedule.
Clear course boundariesThe page explains prerequisites, product scope and the difference between training completion and independent certification. You can compare the offer with your actual requirements.
Compare Brolly Academy with Other Training Institutes
Use the same questions when comparing providers. This course outline gives you specific learning outputs to discuss; confirm each institute's actual delivery and terms before deciding.
What to discuss with Brolly AcademyReview these eight modules and the three project scenarios.
Ask for the assigned trainer profile.
Check the lab version and access period.
Review the fee, schedule and certificate terms.
Use the demo to assess the teaching approach.
What to check with any instituteRequest a detailed outline, not just product names.
Verify the trainer information supplied.
Separate demonstrations from your own lab work.
Check licences, exam costs and refund conditions.
Compare the total commitment, not only the advertised price.
Classroom, Online and Corporate Learning
Discuss the currently available delivery format with the academy before booking. Batch availability and session timings should be agreed in writing.
Hyderabad classroom enquiryAsk about the next classroom batch, venue, system requirements and whether you should bring a laptop.
Live online enquiryCheck the session time zone, remote lab access and arrangements for asking questions or catching up on a missed session.
Corporate team enquiryShare your team size, current tools and learning objectives. Agree a scoped program without sharing confidential business data.
For a team program, explore Brolly Academy corporate training.
SIEM Course Fee and Duration
Contact Brolly Academy for the current fee and timetable for SIEM Training. Review the complete learning commitment and inclusions before you enrol.
Request the current course feeAsk for a written quotation showing the total payable, taxes and payment terms. Confirm whether lab licences, cloud usage or external examination fees are separate.
Confirm the batch timetableDiscuss the instructor-led hours, expected practice time, session dates and access period. The eight-module outline describes the learning sequence, not a fixed completion promise.
Before you enrolCheck lab access, materials, project feedback, missed-session arrangements, refund terms and any additional charges. Keep a copy of the agreed offer.
Course Completion and Certification Guidance
Brolly Academy course completion recognizes the training and assessment work agreed for your batch. It is separate from a credential awarded by a software vendor or another certification body.
Brolly Academy course completionAsk for the attendance, assignment and assessment requirements, the certificate wording and how completion will be verified.
Independent certificationUse official vendor information to check whether a relevant credential is currently offered and what preparation it requires. No vendor authorization, exam voucher or pass guarantee is implied.
Career Roles and Skill Applications
Match the learning path to a role, then compare its requirements with your existing experience. The course can support skill development; it does not guarantee employment.
SIEM analystSearch events and triage detections.
Junior detection engineerDesign and test documented detection logic.
SOC platform contributorSupport source health, parser quality and useful dashboards.
You can also explore Cyber Security Course. Build a broader foundation in security concepts and the responsibilities of a security team.
Where These Skills Are Used
These skills support siem analyst, junior detection engineer, soc platform contributor. Employers combine technical knowledge with careful documentation, communication and responsible access. Your lab portfolio should show decisions, evidence and limitations, not claim that a training exercise was a live client engagement.
Interview and Portfolio Preparation
Prepare evidence you can discuss clearly. Label practice work as training work and do not present a teaching scenario as paid client experience.
Explain a projectDescribe the requirement, your decisions, the result and one limitation. Be ready to answer what you would change for a real deployment.
Show useful evidenceKeep approved files, test results and a concise README or runbook. Remove secrets and private information before sharing a portfolio.
Discuss support servicesAsk the academy which resume, mock-interview or job-search services are included in your batch. Placement assistance is not a job or salary guarantee.
Career Planning and Salary Expectations
Salary depends on the role, prior experience, location and the employer. A tool course alone does not establish a salary band. Compare recent job descriptions, required experience and responsibilities rather than relying on a headline income promise.
Meet the Trainer Through a Demo
Discuss the assigned trainer's relevant experience during a free demo. Ask how they would explain a practical siem problem and review your lab evidence.
Relevant experienceAsk for examples of work with SIEM that can be discussed without revealing confidential client information.
Practical explanationAsk the trainer to explain a failure scenario and how a learner would investigate it, rather than only showing a finished result.
Feedback and supportDiscuss how assignments are reviewed, how questions are handled and the support period included in the course.
Brolly Academy Learner Reviews
Read available academy feedback and ask whether a review relates to this particular course, trainer and delivery format. General academy reviews should not be mistaken for verified results from this new course.
Read Academy ReviewsDownload Your Practice Checklists
Use these editable CSV files to organize your learning. They open in common spreadsheet tools and contain real module and project-checklist content.
Download Syllabus Checklist (CSV) Download Project Review Sheet (CSV)Official Documentation for Further Reading
Use the documentation that matches your product version and environment. These sources support technical learning; linking to them does not imply endorsement of Brolly Academy.
Microsoft Sentinel overview
MITRE ATT&CK red teaming guidance
NIST incident response guidance, SP 800-61 Revision 3
Related Courses at Brolly Academy
Choose complementary learning based on your current skill gaps. These are separate courses, not automatically included in this program.
SOC Analyst CourseConnect technical findings with monitoring, escalation and analyst workflows.
View SOC Analyst Course
Splunk TrainingTake a separate product-focused path when you need deeper Splunk skills.
View Splunk Training
Cyber Security CourseBuild a broader foundation in security concepts and the responsibilities of a security team.
View Cyber Security Course
For a complementary learning path, also explore Incident Response training and Linux Security training. These are separate programs; choose the one that fits your role and prerequisites.
SIEM Training Enquiries in Hyderabad
Speak to Brolly Academy near JNTU Metro Station. The centre address is Metro Pillar No. A689, Dr Atmaram Estates, 3rd Floor, Nizampet X Roads, Hyderabad 500072. Confirm the batch venue before travelling.
Learners from Kukatpally, KPHB, Nizampet, Miyapur and other parts of Hyderabad can contact the academy to discuss classroom or online availability.
Call +91 81868 44555SIEM Training FAQs
How is SIEM different from SOC training?
SIEM is the technology and workflow for collecting, searching and correlating events. SOC work also includes people, escalation, operations and response processes.
Is this the same as Splunk training?
No. This course focuses on detection concepts and evidence. The existing Splunk course provides a separate product-focused learning path.
Which query language will I learn?
It depends on the confirmed lab platform. Discuss whether your batch uses KQL, SPL or another language before joining.
Will AI automatically investigate every alert?
No. Automation can assist, but data quality, context and human review remain important. High-impact response actions need appropriate controls.
What should a detection project contain?
A defined question, source requirements, query logic, benign and suspicious test cases, results, tuning notes and an analyst handover.
Why do SIEM alerts produce false positives?
Rules may lack context, use broad thresholds or receive incorrectly parsed data. Good tuning checks evidence and preserves coverage instead of simply suppressing noise.
What are the course fee and duration?
Contact Brolly Academy for the current batch quotation and timetable. Confirm instructor-led hours, practice time, lab access, taxes and any separate licence or exam charges in writing.
What certificate will I receive?
Ask for the Brolly Academy completion requirements and certificate wording for your batch. Course completion is separate from an independent vendor examination; no external credential or exam voucher is implied.
Request a Free Demo
Share your contact details and the team can discuss course availability, prerequisites and the next suitable session.
Your details are used to respond to this enquiry. Read our Privacy Policy.