
SPL · SIEM · SOC · SPLUNK SOAR
Splunk Training in Hyderabad
Learn Splunk architecture, SPL searches, dashboards, alerts, Splunk Enterprise Security, SOC use cases and Splunk SOAR (Phantom) in a 30-day program with hands-on labs and placement assistance. Classroom and live online batches, weekend options and a free demo class before you enrol.
★ 4+ Google rating from 100+ reviews · 9,000+ students trained · 523+ batches completed · Teaching since 2021
Trainer: Mr. Ramesh Kumar, Splunk SIEM and Cyber Security Specialist (10+ years) · Updated September 2026
TrainerMr. Ramesh Kumar · 10+ years
Duration30 days
FeesFrom ₹6,000
ModesClassroom + online
Splunk Course in Hyderabad
Brolly Academy's Splunk Training in Hyderabad is a 30-day, hands-on program in Splunk architecture, SPL, dashboards, alerts, Splunk Enterprise Security, SOC operations and Splunk SOAR (Phantom), taught by Mr. Ramesh Kumar (10+ years in Splunk, SIEM and SOC operations). Plans start at ₹6,000, classes run in the classroom or live online, and every student gets a course completion certificate and placement assistance.
The course is built for freshers, IT professionals and cybersecurity aspirants. You work with real log data from day one, practise SOC analyst workflows such as alert handling, event correlation and incident monitoring, and finish with a resume, LinkedIn profile and mock interviews for Splunk engineer, SOC analyst and SIEM analyst roles in Hitech City, Madhapur, Gachibowli and Kukatpally.
Why choose Brolly Academy for Splunk training?
Training and support✓ Job-focused Splunk SIEM curriculum
✓ Trainer with 10+ years in Splunk, SIEM and SOC
✓ Hands-on labs with real-time log data
✓ Splunk Phantom and SOAR fundamentals
✓ SOC analyst use cases and alert handling
✓ Real-time dashboards and report building
✓ Resume and interview preparation support
✓ Placement assistance for Splunk roles
Flexibility and value✓ Classroom and live online batches
✓ Weekday and weekend batch options
✓ Free demo class before you enrol
✓ Affordable fees, plans from ₹6,000
✓ Beginner-friendly: no prior Splunk needed
✓ Peer learning with fellow Splunk students
✓ Brolly Academy course completion certificate
✓ 4+ Google rating from 100+ reviews
Splunk Course Syllabus (10 Modules)
Our Splunk training in Hyderabad follows a 10-module syllabus that takes you from Splunk architecture and SPL to dashboards, alerts, Splunk Enterprise Security, SOC monitoring, threat detection and Splunk SOAR (Phantom), finishing with Splunk exam preparation and career readiness.
Module 1: Introduction to Splunk
What Splunk is and its uses in SIEM, SOC and log management, Splunk architecture (indexers, forwarders and search heads), installing Splunk on Windows and Linux, navigating the Splunk Web interface, and configuring data inputs and indexing for logs, network data and files.
Module 2: Search Processing Language (SPL)
Writing and running basic searches, search commands such as stats, eval and rex, filtering, sorting and transforming results, field extraction with regular expressions, and advanced SPL with sub-searches, joins and time-based queries.
Module 3: Data Management & Visualisation
Data ingestion from servers, applications and log sources, building dashboards with charts, tables and graphs, scheduled reports and real-time alerts, search optimisation, and field extractions and lookups for enriched data.
Module 4: Splunk Enterprise Security (ES)
Features of Splunk Enterprise Security, configuring Splunk for real-time security monitoring, security dashboards, correlation searches to detect threats, incident investigation and response, and hands-on labs for live security monitoring.
Module 5: Introduction to Splunk SOAR (Phantom)
Security orchestration, automation and response, integrating Splunk with Phantom, creating playbooks, automating incident response for alerts and incidents, and hands-on SOAR use cases for detection and mitigation.
Module 6: Security Operations Centre (SOC) with Splunk
SOC fundamentals and its role in monitoring and incident response, setting up and monitoring security alerts, real-time threat detection and incident management, and SOC scenarios such as DDoS, brute-force attacks and insider threats.
Module 7: Advanced Security & Threat Detection
Threat hunting in security logs, correlating events across multiple sources, anomaly detection, automated alerts for specific threats, and compliance reporting for GDPR, PCI-DSS and HIPAA.
Module 8: Splunk Cloud & Performance Monitoring
The role of Splunk Cloud in AWS, Azure and GCP environments, configuring cloud data sources for monitoring and event correlation, infrastructure and application performance monitoring, and security monitoring in cloud platforms.
Module 9: Splunk Optimisation & Best Practices
Performance tuning of searches and dashboards for large datasets, data retention and archiving, high-availability setups with Splunk clusters for redundancy and load balancing, and security best practices for Splunk environments.
Module 10: Exam Preparation & Career Readiness
Preparation for Splunk Core Certified Power User, Splunk Admin and Splunk SOAR Certified Automation Developer exams with key topics and practice tests, resume and LinkedIn optimisation, and mock interviews for Splunk engineer, SOC analyst and SIEM roles.
Get the full Splunk syllabus and fee details on WhatsApp
Send us a message and we will share the complete module list, fee plans and the next batch dates. New batches start every week, and a free demo class is available.
Splunk Training Roadmap – Beginner to Job-Ready in 30 Days
Our Splunk course is a 30-day intensive roadmap in 4 practical stages, in the classroom or live online, taking you from basic log analysis to real-time SOC use cases with hands-on practice at every step.
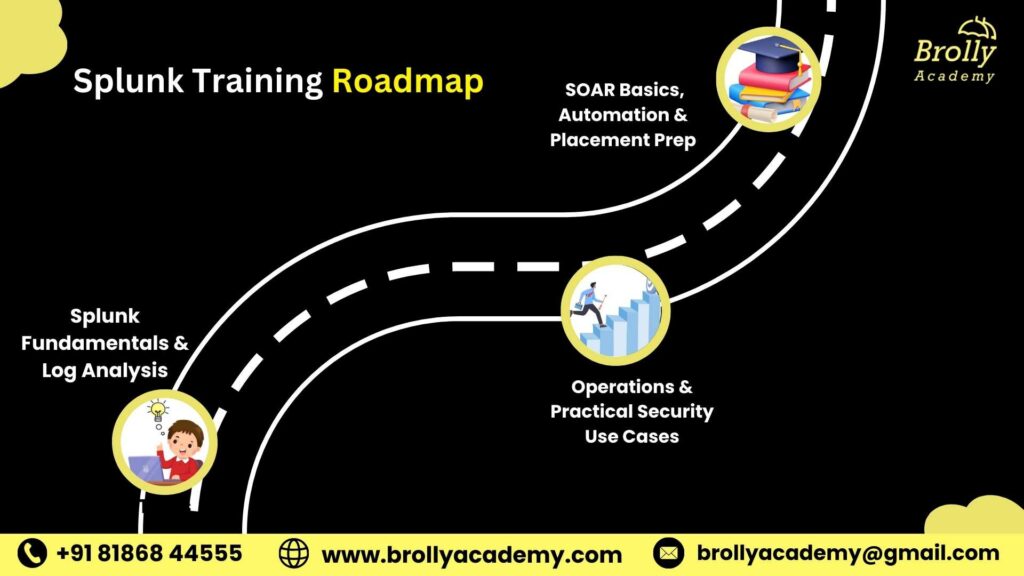
Phase 1Splunk fundamentals & log analysisSplunk and SIEM concepts, architecture, data inputs and indexing, SPL basics, and log ingestion from servers, apps, Kubernetes clusters and security tools.
Phase 2SOC operations & security use casesDashboards, alerts and scheduled searches, security event correlation, SOC analyst workflows, incident detection and Splunk Enterprise Security concepts.
Phase 3SOAR basics & automationAn introduction to Splunk Phantom and SOAR, basic automation workflows, the incident response lifecycle and real-world automation examples.
Phase 4Placement preparationResume preparation for Splunk roles, interview questions, mock interviews and career guidance for Splunk engineer and SOC roles.
What is Splunk and Why Is It Important?
Splunk is a platform used to collect, search and analyse machine-generated data such as logs and events. Using SPL (Search Processing Language), teams find issues and security threats quickly, turn raw logs into dashboards, reports and alerts, and with Splunk SOAR automate incident response. It is widely used in SIEM, SOC operations, IT monitoring and threat detection.
Machine data analyticsCollects, searches and analyses logs and events from any system.
Security and IT operationsUsed for SIEM, SOC operations, monitoring and threat detection.
Many data sourcesGathers data from servers, applications, networks, firewalls and cloud systems.
Real-time searchSPL helps teams find issues and threats quickly.
Dashboards and alertsTurns raw log data into visual dashboards, reports and alerts.
Threat detectionHelps SOC analysts spot suspicious activity, attacks and incidents.
Automation and responseSplunk Phantom and SOAR automate incident response workflows.
Reliability and complianceEnterprises use Splunk for system reliability, security and compliance.
Used across industriesBanking, healthcare, e-commerce, telecom, cloud and government teams rely on it.
Benefits of the Splunk Course in Hyderabad
Choose classroom or live online training at Brolly Academy and get the same experienced trainer, hands-on SIEM and SOC practice and placement support in either mode.
01Learn from a Splunk and SIEM expertTraining from a professional with real-world SOC and cybersecurity experience.
02Hands-on SIEM and SOC trainingLog analysis, dashboards, alerts and incident monitoring as used in real companies.
03Real-time security use casesPractise SOC scenarios, threat detection and monitoring workflows.
04Job and placement supportResume preparation, interview questions and Splunk job guidance.
05Job-ready skillsSkills aligned with Splunk engineer and SOC analyst roles.
06Dashboard and reporting skillsCreate visual dashboards and reports from raw machine data.
07Automation and SOAR basicsSplunk Phantom and SOAR fundamentals for incident response automation.
08Beginner-friendly learningNo prior Splunk experience needed; concepts are explained step by step.
09Learn your wayClassroom or online, weekday or weekend batches, at an affordable fee.
Thinking of Splunk Training in Hyderabad?
Here is how hands-on training at Brolly Academy compares with a traditional class.
Traditional training✗ Outdated syllabus with a limited SIEM scope
✗ Mostly theory-based sessions
✗ Minimal exposure to real SOC use cases
✗ No personalised trainer guidance
✗ Basic tools with limited access
✗ No automation or SOAR concepts
✗ Weak or no placement assistance
✗ Fixed batch timings
Brolly Academy training✓ Updated curriculum with Splunk SIEM and SOAR
✓ Hands-on training from day one
✓ Real-time SOC and security projects
✓ One-on-one mentor support and doubt clearing
✓ Practice in Splunk lab environments
✓ Modern dashboards, alerts and workflows
✓ Resume, LinkedIn and interview prep included
✓ Flexible online and classroom batches
Meet Your Splunk Trainer
INSTRUCTOR
Mr. Ramesh Kumar
Splunk SIEM & Cyber Security Specialist · 10+ years in Splunk, SIEM and SOC operations
Mr. Ramesh Kumar is a Splunk SIEM and cyber security specialist with 10+ years of experience in Splunk, SIEM and SOC operations. His expertise covers log analysis, dashboards, alerts, Splunk Enterprise Security, Splunk Phantom and SOAR. His project work includes real-time SOC monitoring, threat detection use cases, incident response workflows, security dashboards and enterprise log monitoring solutions. He explains complex Splunk and SIEM concepts in a simple, practical way, with hands-on labs, real-time use cases and job-focused training.
Skills You’ll Gain from the Splunk Course
Machine data managementCollect, index and manage machine data in Splunk.
SPL queriesWrite efficient SPL searches for log search and analysis.
Dashboards and reportsBuild real-time dashboards and visual reports.
AlertingConfigure alerts for security and operational events.
Log analysisAnalyse logs from servers, apps, networks and cloud.
SOC workflowsPerform SOC analyst workflows and incident monitoring.
Threat detectionCorrelate events for threat detection and SIEM use cases.
Enterprise Security and SOARSplunk ES fundamentals and Phantom automation basics.
IT operations monitoringApply Splunk to performance and application health monitoring.
Splunk Capstone Projects
You build portfolio-ready projects that show employers how you use Splunk for log analysis, SOC monitoring, threat detection and automation, in the classroom or online.
Project 1Log monitoring and analysisIngest, index and search real-time logs from servers and applications with SPL.
Project 2SOC alerting and incident monitoringAlerts and scheduled searches that detect suspicious activity in a simulated SOC.
Project 3Security dashboards and reportingInteractive dashboards for security events, system health and operational metrics.
Project 4SIEM use case implementationDetect brute-force attacks, login anomalies, malware indicators and policy violations.
Project 5Threat detection and event correlationCorrelate events from multiple sources and reduce false positives.
Project 6SOAR and automation basicsBasic Splunk Phantom and SOAR workflows that streamline incident response.
Tools you use: Splunk Enterprise · Splunk Cloud Platform · Splunk Enterprise Security · Splunk SOAR (Phantom) · Splunk REST API · Splunk alerts · Splunk lookups · Splunk apps (Splunkbase)
Splunk Course Fee & Offerings in Hyderabad
Choose the plan that suits how you learn. Every plan covers Splunk from basics to SIEM and SOC use cases, with resume and interview support.
Video Recording₹6,000Was ₹10,000
Complete Splunk basics to advanced
SPL (Search Processing Language) training
Log analysis and dashboards
SIEM and SOC fundamentals
60+ recorded sessions
Real-time use case explanations
Resume and interview guidance
Lifetime video access
WhatsApp support group
Most popularClassroom Training₹12,000Was ₹20,000
Experienced Splunk and SOC trainer
Hands-on labs from day 1
Real-time SOC and SIEM projects
Dashboards, alerts and reporting
Splunk Phantom and SOAR basics
One-on-one mentor support
Weekly mock interviews
Resume and LinkedIn optimisation
Dedicated placement assistance
WhatsApp and doubt-clearing support
Online Course₹10,000Was ₹16,000
Live interactive online classes
30-day structured Splunk training
Flexible batch timings
Real-time labs and SOC use cases
Daily class recordings
Weekly mock interviews
Resume and interview preparation
Placement assistance
WhatsApp group access
Ask about the current batch offer and payment options when you book your free demo class. Splunk certification exam fees are paid separately to Splunk.
Placement Program for Splunk Training in Hyderabad
Our placement assistance helps you finish the course job-ready and get interviews for SOC, SIEM and cyber security roles in Hyderabad and across India.
Resume buildingATS-friendly resumes focused on Splunk engineer and SOC analyst roles.
Placement trainingJob-oriented training aligned with Splunk, SIEM and SOC requirements.
Interview question bankPractise real Splunk, SIEM and SOC interview questions.
Internships under expertsHands-on internship exposure with security and monitoring projects.
Real-time projectsLog analysis, dashboards, alerts and SOC use cases in Splunk.
Aptitude preparationLogical reasoning, problem-solving and technical aptitude.
Personality developmentCommunication, confidence and interview readiness.
Mock interviewsMultiple mock interviews with industry professionals.
Interview schedulingWe help schedule interviews and support you through to an offer.
What Our Students Say About Splunk Training in Hyderabad
"I am very happy with the training I received at Brolly Academy. The instructors were patient, diligent and helpful at all times. They kept us engaged in class with relevant examples and tips for real-world situations. The content was well organised and easy to understand. I would recommend this course to anyone who wants to learn Splunk."Priyanka
"I took the Splunk training online and it was a great experience. The trainer was clear and concise in explaining concepts, and the course material was comprehensive enough to help me get started with Splunk. I would recommend this course to others looking for hands-on experience with Splunk."Abhishek
"The course was very well structured, and the instructor was very knowledgeable. He gave real-world examples of how to apply Splunk in different scenarios. The course material was also very helpful and comprehensive. I would recommend this course to anyone looking to learn Splunk."Prashant
"Splunk is a powerful tool that can be used for many purposes. I attended this course, and I am glad to say it was worth every penny. The instructor was very knowledgeable and gave us real-world examples of how Splunk can be used in different scenarios."Rahul
Student community
Learning & collaborationWork with fellow students on Splunk labs, SOC use cases, dashboards and projects.
Resources and toolsSplunk learning materials, use-case documents, recorded sessions and practice labs.
NetworkingConnect with Splunk learners, SOC analysts, cybersecurity professionals and recruiters in Hyderabad.
MentorshipGuidance from Splunk experts on real-world SOC challenges and best practices.
Career developmentSplunk job openings, interview opportunities, live projects and placement assistance.
Pre-requisites & Eligibility
Our Splunk training is designed for learners from different educational and professional backgrounds, whether you want to start a cybersecurity career, move into SOC roles or upgrade your IT skills. No prior Splunk, SIEM or coding experience is required; a basic understanding of servers, logs or networking helps and is covered during training.
No advanced skills requiredNo prior Splunk or SIEM knowledge is needed to join.
Students & graduatesGraduates from any stream who want SOC, SIEM or cybersecurity roles.
FreshersBeginners who want to build a career using Splunk.
Working professionalsSystem admins, network engineers, IT support and software professionals upskilling.
Freelancers & business ownersAdd Splunk SIEM skills or monitor systems, logs and security events.
Basic IT knowledge helpsServers, logs and networking basics are an advantage, and covered in class.
Who Should Learn Splunk?
Fresh graduatesStudents from any degree who want to start in cybersecurity or SOC operations.
Job seekers & career switchersProfessionals planning to move into Splunk, SIEM or cybersecurity roles.
Working IT professionalsSystem admins, network engineers and IT support staff upgrading their skills.
Cyber security aspirantsAnyone interested in threat detection, monitoring and incident response.
SOC analyst beginnersThose aiming to work in security operations centres.
Splunk engineer candidatesCandidates targeting Splunk engineer, SOC analyst and SIEM analyst roles.
Splunk Career Opportunities in Hyderabad
Splunk engineerBuild, manage and optimise Splunk environments, dashboards and alerts.
SOC analystMonitor security events, investigate incidents and respond to threats.
SIEM analystAnalyse logs, correlate events and improve security visibility.
Cyber security analystIdentify vulnerabilities, detect attacks and support incident response.
Splunk SOAR engineerAutomate incident response workflows with Splunk Phantom and SOAR.
Cloud security analystMonitor cloud infrastructure logs and security events with Splunk.
Splunk engineer salary in Hyderabad – 2026
Splunk engineer₹4–25 LPAFreshers ₹4–6 LPA · mid-level ₹8–12 LPA · experienced ₹15–25 LPA+
SOC analyst (Splunk)₹3.5–18 LPAFreshers ₹3.5–5.5 LPA · mid-level ₹7–10 LPA · experienced ₹12–18 LPA+
SIEM analyst₹4–20 LPAFreshers ₹4–6 LPA · mid-level ₹8–11 LPA · experienced ₹14–20 LPA+
Splunk SOAR engineer₹5–30 LPAFreshers ₹5–7 LPA · mid-level ₹10–15 LPA · experienced ₹18–30 LPA+
Cloud security analyst₹5–28 LPAFreshers ₹5–7 LPA · mid-level ₹10–14 LPA · experienced ₹18–28 LPA+
Hiring companiesWhere students applyGoogle · Microsoft · TCS · Infosys · Wipro · HCLTech · Tech Mahindra · Capgemini · Accenture · Deloitte · IBM · Cognizant · Oracle · SAP · Flipkart · Mphasis
Splunk Certification You Will Receive
After completing the course you receive a Brolly Academy Splunk course completion certificate that highlights your skills in SPL, log analysis, dashboards, alerts, SOC workflows and Splunk SOAR basics. Classroom and online students receive the same certificate, and together with your projects it strengthens your resume for SIEM, SOC and cyber security roles.
Splunk certification exams: the course prepares you for Splunk exams such as Splunk Core Certified Power User, Splunk Enterprise Certified Admin and Splunk SOAR Certified Automation Developer. These certifications are issued and examined by Splunk, not Brolly Academy, and exam fees are separate.
Market trends for Splunk in Hyderabad
SOC and SIEM rolesSteady demand for SOC analysts and SIEM engineers across industries.
Rising cyber threatsGrowing threats keep security monitoring skills in demand.
Cloud securitySplunk Cloud is used to monitor events in AWS, Azure and Google Cloud.
Certification interestWider Splunk adoption increases interest in Splunk certifications.
New industriesTelecom, finance and healthcare invest in Splunk for proactive security.
Security automationSOAR skills are sought for automated incident response.
Splunk Training in Kukatpally, Hyderabad
Our centre is at Metro Pillar No. A689, Dr Atmaram Estates, 3rd Floor, Nizampet X Roads, near JNTU Metro Station, Hyderabad 500072. Students join from Kukatpally, KPHB Colony, JNTU, Nizampet, Miyapur, Hitech City, Madhapur and Ameerpet (a short metro ride). Can’t make it to class? Join the same course live online.
Other relevant courses
SOC AnalystSecurity monitoring, incident response and SOC workflows.
Cyber SecurityNetwork security, threats and defence fundamentals.
CyberArkPrivileged access management with CyberArk.
Ethical HackingPenetration testing and ethical hacking techniques.
SQLQuery and manage data in relational databases.
Power BIDashboards and business reporting with Microsoft Power BI.
Splunk Training in Hyderabad – FAQs
1. What is the fee for Splunk training in Hyderabad?
Brolly Academy offers three Splunk plans: Video Recording at ₹6,000 (was ₹10,000), Online Course at ₹10,000 (was ₹16,000) and Classroom Training at ₹12,000 (was ₹20,000). The live plans include real-time labs, weekly mock interviews and placement assistance. Splunk certification exam fees are separate and paid to Splunk. Ask about the current offer at your free demo.
2. How long does it take to learn Splunk at Brolly Academy?
The Splunk course runs for 30 days. You start with Splunk fundamentals, SPL and log analysis, move into dashboards, alerts, SOC workflows and Splunk Enterprise Security, then learn Splunk SOAR basics and finish with resume preparation and mock interviews. Weekday and weekend batches run in the classroom and online.
3. Which is the best Splunk training institute in Hyderabad?
Brolly Academy is a strong choice for Splunk training in Hyderabad. You learn from Mr. Ramesh Kumar, who has 10+ years in Splunk, SIEM and SOC operations, follow a 10-module syllabus from SPL to Enterprise Security and SOAR, build six SOC-focused projects, and get placement assistance, in the classroom near JNTU or live online.
4. What is covered in the Splunk course syllabus?
The syllabus covers Splunk architecture and installation, data inputs and indexing, SPL searches and field extraction, dashboards, reports and alerts, Splunk Enterprise Security, Splunk SOAR (Phantom) playbooks, SOC monitoring, threat hunting and compliance reporting, Splunk Cloud, performance tuning and clustering, and preparation for Splunk certification exams and interviews.
5. What are the prerequisites for Splunk training?
There are no formal prerequisites. You do not need prior Splunk, SIEM or coding knowledge to join. A basic understanding of IT systems, servers, logs or networking is an advantage, but these basics are covered during training. What matters most is regular practice in the hands-on labs and interest in security and monitoring.
6. Can freshers and non-IT graduates learn Splunk?
Yes. The course is designed for beginners and explains concepts step by step, starting from what Splunk is and how logs are collected. Graduates from any stream who want to enter cybersecurity, SOC or SIEM roles can join. SPL is taught from scratch, and hands-on labs help you build confidence before you work on projects.
7. What is the salary of a Splunk engineer in Hyderabad?
Splunk engineers in Hyderabad typically earn around ₹4–6 LPA as freshers, ₹8–12 LPA at mid-level and ₹15–25 LPA or more with experience. SOC analysts with Splunk skills start at about ₹3.5–5.5 LPA, and Splunk SOAR engineers at ₹5–7 LPA. Actual pay depends on your skills, projects and employer.
8. Does Brolly Academy provide placement support for Splunk students?
Yes. Placement assistance includes ATS-friendly resumes for Splunk engineer and SOC analyst roles, placement training, Splunk, SIEM and SOC interview questions, internships under experts, real-time projects, aptitude preparation, personality development, mock interviews with industry professionals and interview scheduling support until you receive offers in Hyderabad and across India.
9. Will I get a Splunk certificate after the course?
Yes. You receive a Brolly Academy Splunk course completion certificate. The course also prepares you for Splunk exams such as Splunk Core Certified Power User, Splunk Enterprise Certified Admin and Splunk SOAR Certified Automation Developer. Those certifications are issued and examined by Splunk, not Brolly Academy, and the exam fees are paid separately.
10. Can I learn Splunk online or in a classroom in Hyderabad?
Both. Brolly Academy offers classroom Splunk training at our centre near JNTU Metro Station and live, instructor-led online classes with daily recordings and flexible timings. A self-paced Video Recording plan with 60+ recorded sessions is also available. The syllabus, labs and placement assistance are the same in the classroom and online.
11. What tools will I learn in the Splunk course?
You work with Splunk Enterprise, Splunk Cloud Platform, Splunk Enterprise Security and Splunk SOAR (Phantom), and learn SPL, alerts, lookups, dashboards, the Splunk REST API and apps from Splunkbase. Labs use real log data from servers, applications, networks and security tools, including Kubernetes environments, so you practise the way SOC teams work.
12. What is the difference between Splunk and Splunk SOAR?
Splunk is a log analysis and monitoring platform used to collect, search and visualise machine data and detect threats. Splunk SOAR, formerly Phantom, focuses on security orchestration, automation and response: it runs playbooks that automate repetitive incident response tasks and connect security tools. Our course teaches Splunk first, then SOAR basics.
13. What projects will I build in Splunk training?
You build six projects: log monitoring and analysis with SPL, SOC alerting and incident monitoring, security dashboards and reporting, SIEM use cases such as brute-force attacks and login anomalies, threat detection through event correlation, and basic Splunk Phantom and SOAR automation workflows that streamline incident response. These projects form your portfolio for interviews.
14. Is Splunk good for a cybersecurity career?
Yes. Splunk is widely used in SIEM, SOC and incident response work across IT, banking, telecom, healthcare and cloud companies. After training you can apply for Splunk engineer, SOC analyst, SIEM analyst, cyber security analyst and Splunk SOAR engineer roles, and grow into senior security operations positions as you gain experience.
15. Is there Splunk training near me in Kukatpally or JNTU?
Yes. Brolly Academy is at Metro Pillar No. A689, Dr Atmaram Estates, 3rd Floor, Nizampet X Roads, near JNTU Metro Station, Hyderabad 500072. Students join from Kukatpally, KPHB Colony, Nizampet, Miyapur, Hitech City, Madhapur and Ameerpet. If travel is difficult, you can join the same Splunk course live online.
Got more questions? Talk to our team directly
Contact us and our academic counsellor will get in touch with you shortly. A free demo class is available before you enrol.